Edgeweir: Open-Source, Self-Hosted CDN / WAF Control Plane; Console + Edge Nodes Fully Open Source, No Feature Restrictions
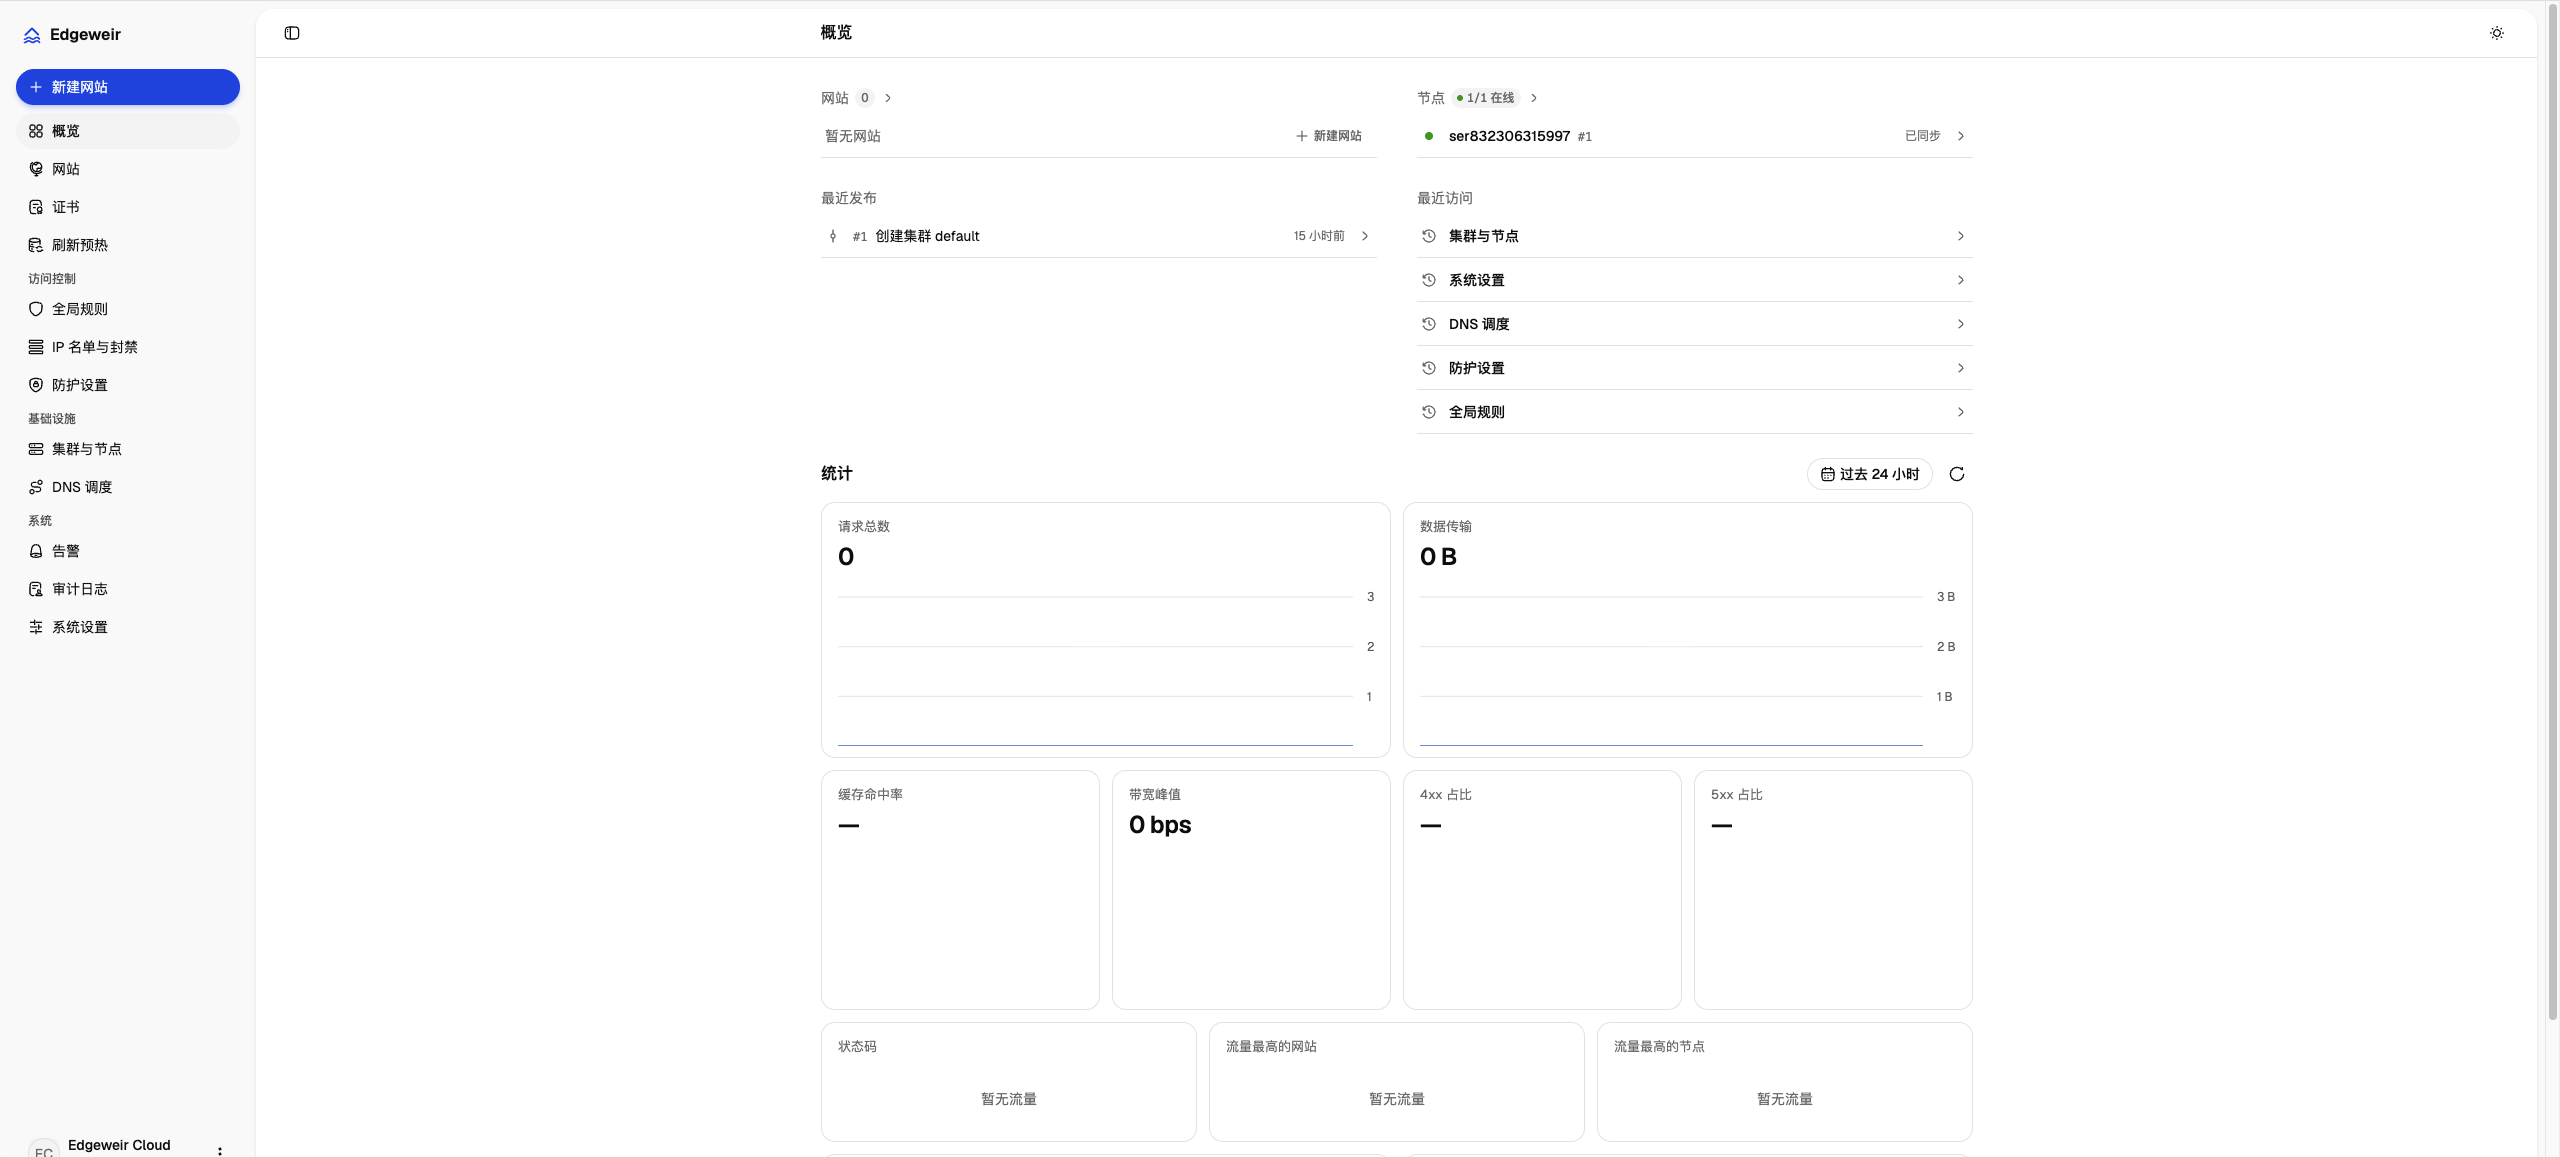
GitHub:
Nodes:
Documentation:
Website:
If you find it useful, give it a Star
— it would mean a lot.
Why I Built It
- There was no open-source, free, fully featured CDN control plane: WAF, CC protection, traffic scheduling, and node count should not be locked behind a license
- The GoEdge supply-chain poisoning incident: after the management console was compromised, malicious scripts were distributed via SSH to all nodes and injected into users’ websites. A CDN sits in the middle of all traffic, so its control plane must be open source and auditable
Security Design
- The console does not store SSH credentials and has no remote execution channel
- Node private keys are generated locally and never leave the node; mTLS is used throughout after registration
- Registration tokens are single-use and only their SHA-256 hashes are stored
- cosign signature verification + per-package SHA-256 verification before node installation; console images are cosign-signed
- Certificate private keys and DNS API keys are stored using envelope encryption
- No callbacks, license checks, or telemetry
Features
- Origin and Caching: origin pools / origin groups, active + passive health checks, session persistence, S3-signed origin pulls, WebSocket, expression-based cache rules, slicing, purging by URL / directory / Host / Cache-Tag, sitemap prewarming
- HTTPS: automatic issuance and renewal via ACME HTTP-01 / DNS-01, HTTP/2, HTTP/3, Brotli / Zstd / Gzip
- WAF: OWASP CRS (paranoia level, anomaly score thresholds, exclusions by rule ID), staged rules, rate limiting, redirects / rewrites, request and response header transformations
- CC Protection: four levels of challenges—Cookie / JS / PoW / image CAPTCHA—Under Attack mode, automatic tiered CC escalation at the node level, JA4 fingerprinting, IP blocking within seconds (global blocking via nftables kernel packet drops)
- Layer 4 Forwarding: TCP / UDP port pools, PROXY protocol v1 / v2, connection limits, add or remove ports without dropping connections
- Traffic Scheduling: regional probes, automatic removal of nodes based on node metrics, backup node groups / backup IPs, carrier routes (DNSPod, Tencent Cloud, Alibaba Cloud, Huawei Cloud)
- Operations: access logs and CSV export, optional ClickHouse, OpenAPI, 2FA / Passkey, audit logs, signed canary upgrades and rollbacks for nodes, backup and recovery
Architecture
- Console: a single Node.js process and image, with PostgreSQL 18 as its sole dependency
- Nodes: Go agent + OpenResty, amd64 / arm64, Debian 12+ / Ubuntu 22.04+ / RHEL 9+
- Console and nodes: protobuf contract, Connect-RPC over mTLS
- End-to-end tests cover registration, deployments, caching, failover, challenges, CC, CRS, ban deployment (p95 ≤ 5s), Layer 4 forwarding, and traffic scheduling
Deployment
Supports Docker Compose, BaoTa / aaPanel, Railway, Fly.io, and bunny.net. The console generates the node installation command; connect a node with a single command.
Notes
- AGPL-3.0, suitable for compliant commercial use
- More features are under continuous development; Issues and forum feedback are welcome
One more request for a Star
