An open-source serverless Web SSH tool built on Cloudflare Workers—just open your browser, connect to your server, and get to work.

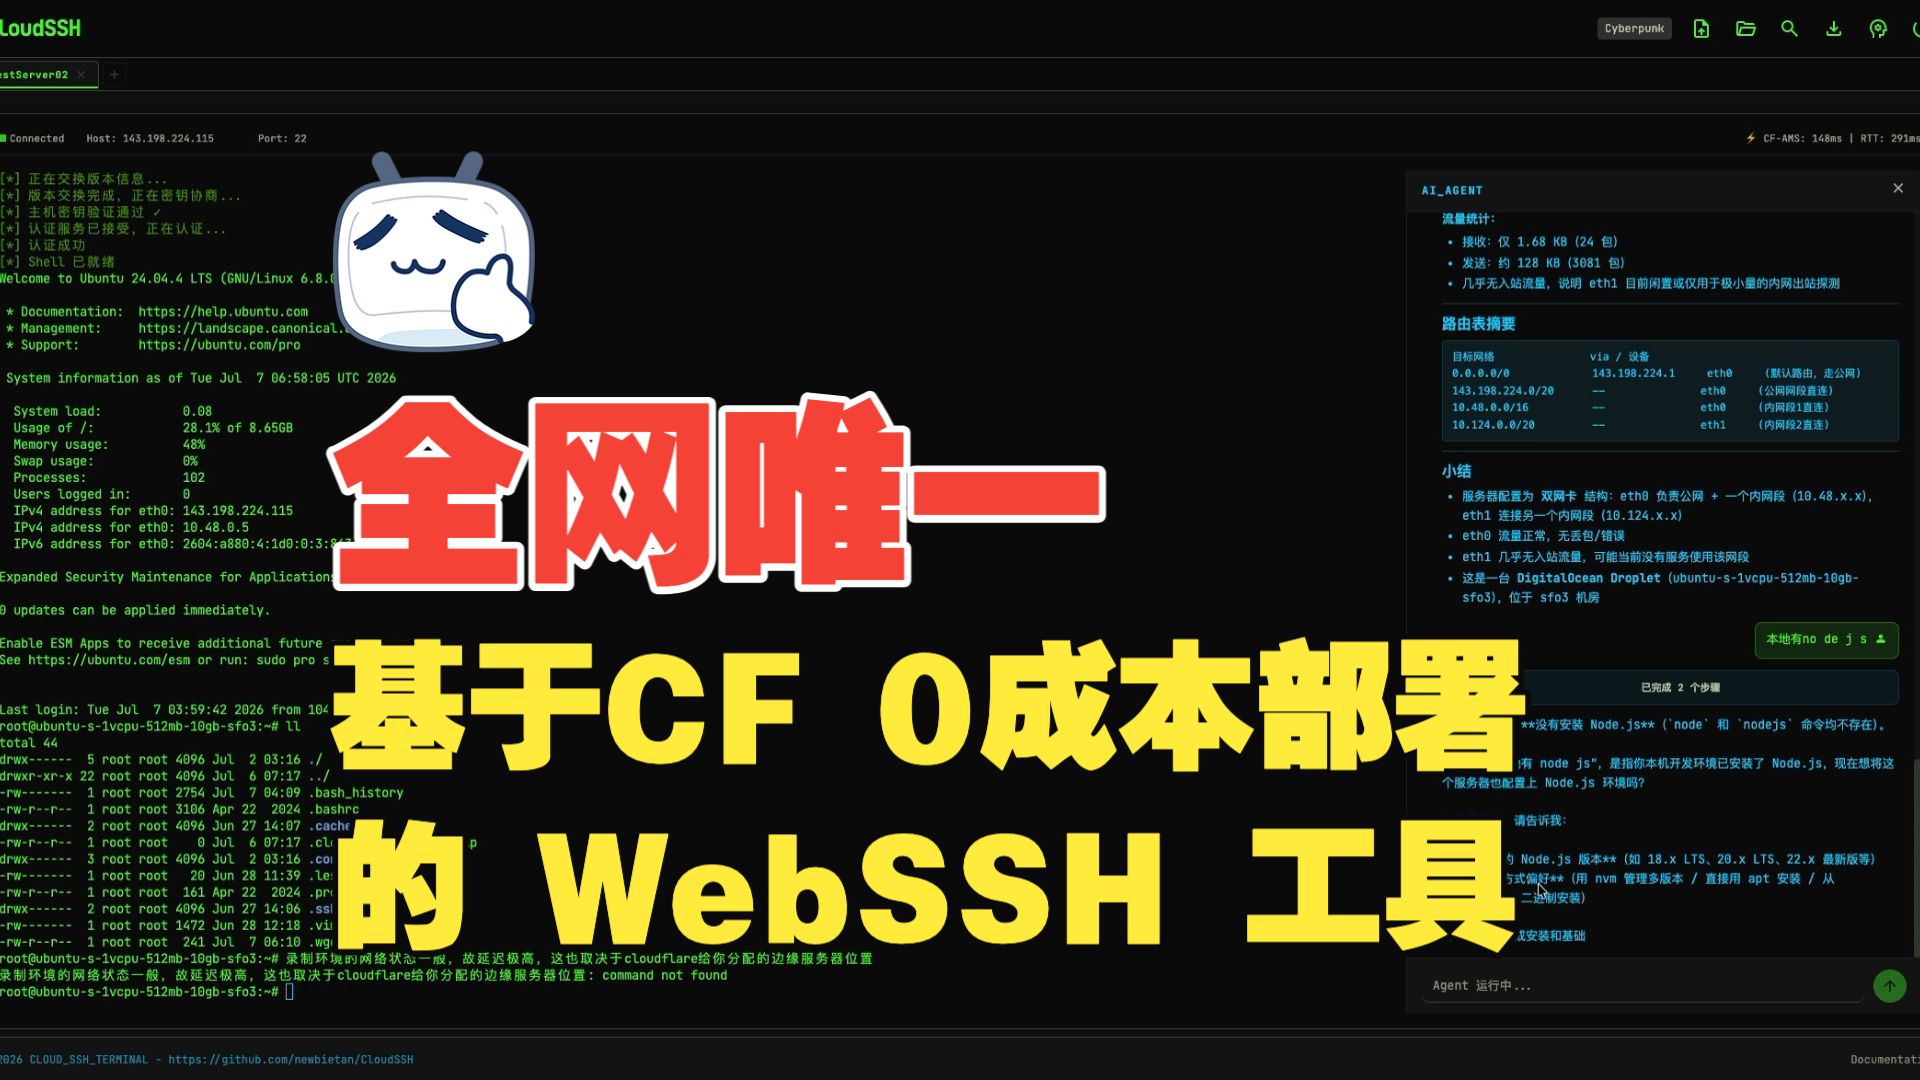
Video demo below:
Background
Have you ever run into this: You’re out and suddenly get a server alert on your phone, but you don’t have your laptop, or the borrowed computer doesn’t have an SSH client. By the time you’ve installed tools, configured keys, and connected, the best moment for action may have passed.
Or maybe you just want to check server status quickly, but you still have to:
Open terminal → Find server config → Enter command → Complete task → Close terminal.
The process isn’t long, but repeat it every day and it gets tedious.
So I made CloudSSH—a serverless Web SSH tool running on Cloudflare Workers.
No need to install a separate SSH client or rent a jump server. Open your browser and you can connect to and manage your servers.
What exactly is it?
In short: It brings an SSH terminal, SFTP file manager, and AI Ops assistant together into your browser.
CloudSSH leverages Cloudflare Workers’ TCP Sockets feature to establish TCP connections between Cloudflare edge nodes and target SSH servers, and implements SSH-2.0 entirely in TypeScript.
The basic data pipeline:
Browser
  │
  │ HTTPS / WebSocket
  ▼
Cloudflare Worker
  │
  ▼
SSHSessionDO
  │
  │ SSH / TCP Socket
  ▼
Your server
It’s not just a web terminal for commands, it currently supports:
- Multi-tab SSH sessions in one page
- Graphical SFTP file management
- trzsz CLI file transfer
- GitHub OAuth login and server management
- Custom themes & online theme editor
- AI agent operations assistant
- Smart region scheduling and latency display
- Terminal search & log export
- Chinese and English interface
Why is it worth using?
No extra backend server maintenance
CloudSSH’s backend runs on Cloudflare Workers and Durable Objects, so you don’t need to maintain traditional web services, reverse proxies, or SSH jump servers.
For personal and lightweight use cases, you can take advantage of Cloudflare’s free quota. For details on quotas and pricing, refer to Cloudflare’s latest official documentation.
Simple deployment
CloudSSH recommends binding your GitHub repo via the Cloudflare Dashboard for one-click deployment—no manual commands needed.
Steps:
- Fork the CloudSSH repo to your GitHub account.
- Log into the Cloudflare Dashboard and go to Workers & Pages.
- Create an application and connect to GitHub, then choose the repo you just forked.
- Set the production branch to
main. - Set the build command:
pnpm run build:frontend
- Save and start deployment.
After deploying, Cloudflare provides a workers.dev access URL. You can also bind your own domain via Settings → Domains & Routes.
Optional features
To enable GitHub login and cloud server management, set these in the Worker’s Settings → Variables and Secrets:
GITHUB_CLIENT_ID
GITHUB_CLIENT_SECRET
BASE_URL
To enable Cloudflare Turnstile verification, set:
TURNSTILE_SECRET
TURNSTILE_SITEKEY
Sensitive configs like GITHUB_CLIENT_SECRET and TURNSTILE_SECRET should be stored as Secret type.
If you don’t configure GitHub OAuth or Turnstile, anonymous SSH still works; related features are hidden by default.
Security: Understanding the boundaries
The most common question about Web SSH is: Is it safe?
CloudSSH is not just Telnet in a web page—it implements the full SSH-2.0 stack and multiple security measures.
But security isn’t just about conclusions: it’s also about understanding how credentials are processed.
SSH protocol and encryption
CloudSSH implements SSH-2.0 in pure TypeScript, not relying on third-party SSH client libraries. It currently supports:
- Curve25519-SHA256 key exchange
- ECDH-NISTP256 key exchange
- AES-256-GCM, AES-128-GCM
- AES-256/192/128-CTR
- HMAC-SHA2-256/512, HMAC-SHA1
- Ed25519, ECDSA P-256, RSA host key verification
- Password authentication
- Ed25519 private key authentication
Browser-to-Cloudflare uses HTTPS/WSS encryption; Cloudflare-to-server uses SSH encryption.
Note: Since SSH runs in the Worker, it’s two encrypted links—not native end-to-end SSH from browser to target server.
TOFU host key verification
On first connection, CloudSSH calculates and displays the server’s host key SHA-256 fingerprint and records it:
- Anonymous users: stored locally in the browser
- Logged-in users: also stored in the cloud account
On reconnecting, fingerprints are compared. If the server’s host key changes, CloudSSH blocks the connection to avoid unknowingly connecting to a replaced or MITM server.
This is a standard TOFU (Trust On First Use) approach: record on first use, enforce verification later.
How are credentials stored and transmitted?
Anonymous user connections and authenticated (GitHub) user connections use different processes.
Anonymous
Anonymous users enter passwords/private keys in the browser, which are sent to the Cloudflare Worker via same-origin WebSocket.
If “Remember connection info” is checked, CloudSSH uses PBKDF2 to derive a key and AES-256-GCM to encrypt credentials, storing up to 5 records in browser localStorage.
If unchecked, credentials are not saved locally.
Logged-in users
Credentials saved after GitHub login are encrypted with AES-256-GCM and stored in UserDBDO.
When connecting:
- UserDBDO decrypts the credentials inside the service.
- Generates a one-time connection token valid for 60 seconds.
- The browser only gets this token.
- The Worker uses the token internally to pass credentials to SSHSessionDO.
- Token is invalidated after use.
So, the decrypted password/private key never goes back to the browser or the URL.
SSRF and DNS rebinding protection
For SSH and AI services, SSRF protection includes:
- Filtering private/loopback/reserved IPv4 addresses
- Filtering loopback, link-local, and unique-local IPv6
- Filtering IPv4-mapped IPv6, etc.
- Cloudflare DoH used to resolve domains; all results are checked
- Prevents DNS rebinding to internal addresses
- Blocks unauthorized AI service redirects
- Restricts some high-risk ports
This means CloudSSH can’t be used as an intranet scanner or cloud metadata proxy by default.
Connection rate-limiting and human verification
/api/ssh endpoints have per-Worker in-memory rate limits to smooth spikes and avoid unbounded growth under load.
Note: This rate limit is for traffic control—not full authentication. Actual connect authorization is via:
- Cloudflare Turnstile
- GitHub login session
- One-time connection token
- Same-origin WebSocket origin checks
Turnstile is optional, but helps prevent bot and abusive use.
Terminal experience: More than just entering commands
The terminal uses xterm.js with WebGL rendering, and supports interactive/TUI apps like Vim or Vi.
Currently provides:
- Multi-tab SSH sessions per page
- Independent session and terminal status per tab
- Auto window resize sync
- Search in terminal text
- Export complete terminal logs
- Disconnection status alert
- Cloudflare Colo display
- Client-to-Cloudflare RTT
- Cloudflare-to-server connection latency
- Structured, internationalized SSH status messages
Each tab has independent terminal, SFTP, and Agent state—switching doesn’t mix up sessions.
File transfers: Both CLI and GUI supported
Method 1: trzsz command line
CloudSSH integrates trzsz.js.
On your server, after installing trzsz, just run:
trz
To upload, or:
tsz filename
To download.
Also supports:
- Drag-and-drop to upload
- Directory transfers
- Resume by breakpoint
- tmux session compatibility
Method 2: SFTP GUI (Recommended)
A pure TypeScript SFTP v3 client is built-in and runs in parallel with the terminal via SSH subsystem channels.
Supports:
- Directory browsing
- Upload files
- Download files
- Create folders
- Rename
- Delete files or dirs
- Concurrent downloads
- Upload task tracking/cancel
- Large directory protection
If you don’t like typing commands, just use the browser for file management.
AI Agent: The terminal assistant
CloudSSH has a built-in AI Agent for operations.
After login, you can set your own OpenAI-compatible base URL, API Key, and model. Supports OpenAI, DeepSeek, Qwen, Kimi, OpenRouter and compatible services.
The agent reads current terminal context and executes tasks via a separate SSH Exec Channel. It now provides 8 tools:
- Run command
- Read terminal context
- Detect server environment
- List processes
- Manage systemd services
- Manage Docker containers
- User confirmation
- Generate structured replies
Multistep jobs display real-time reasoning and execution progress, auto-collapsing at the end (but expandable).
Agent security
The AI Agent doesn’t just run any command—it enforces:
- Rejects destructive commands like
rm -rf /, fork bombs,mkfs, etc. - Requires user confirmation for high-risk actions
- Users can stop the Agent at any time
- Confirmation pauses timeout
- LLM output and tool results are sanitized
- AI service Base URL is SSRF- and DNS-checked
- External service redirects are blocked by default
- API keys are encrypted at rest
AI can still make mistakes—use it as an assistant, not a fully autonomous sysadmin.
UI: Cyberpunk, but more than just cyberpunk
CloudSSH uses the Cyberpunk theme by default, but also includes:
- Cyberpunk
- Glacier
- Gruvbox
All colors are CSS-variable driven. Custom JSON themes are supported.
A visual online theme editor is available at:
The editor follows the latest UI, with real-time preview for:
- Anonymous connect page
- User space & server list
- Add-server dialog
- Multi-tab terminal
- SFTP manager
- AI Agent panel
You can export/import JSON themes and logged-in users can sync to the cloud for cross-browser use.
Both the theme editor and main UI support Chinese and English.
Internationalization
CloudSSH supports simplified Chinese and English for:
- Anonymous connection
- Server management
- Terminal statuses
- Host key prompts
- SFTP manager
- AI settings
- Agent dialog and job status
- Toasts, confirmations, modals
- Online theme editor
Language selection is persisted locally and overrideable via URL param.
To avoid session context mismatch, you can’t switch language mid-session; pre-session selection is respected.
The Agent will also reply in the current UI language, but will not translate commands, paths, or code.
GitHub login & cloud server management
CloudSSH supports optional GitHub OAuth login.
Once configured, users can:
- Save favorite servers
- Edit/delete servers
- One-click connect
- Cloud-save TOFU host fingerprints
- Sync custom themes
- Save AI model configs
- Store connection region hints
Without GitHub OAuth, anonymous SSH works as usual.
OAuth session cookies use:
HttpOnlySecureSameSite=Lax
And use OAuth state for CSRF prevention.
Smart region scheduling
When saving servers, CloudSSH can infer the best Durable Object region based on the target server, and saves this to the DB.
Connections just read the saved locationHint—no need for per-connect geo lookups.
Region selection priority:
User manual selection
        ↓
System-inferred region
        ↓
Cloudflare automatic scheduling
Anonymous users can also choose a region.
Note: Cloudflare’s locationHint is a best-effort feature. It may assign elsewhere if a region is overloaded.
How is it implemented?
The core uses Cloudflare Workers’ cloudflare:sockets to connect to SSH servers directly from edge nodes, and implements SSH handshake, key exchange, auth, channels, and data in TypeScript.
Key tech stack: Cloudflare Workers, TypeScript, etc.
Project structure:
src/
├── ssh/                    SSH-2.0 & SFTP v3 protocol
└── worker/
    ├── index.ts            Worker routing/auth/connect entry
    ├── durable-object.ts   SSHSessionDO
    ├── user-db.ts          UserDBDO
    ├── ssh-session.ts      SSH state/channels
    ├── sftp-handler.ts     SFTP jobs/queue
    └── agent/              AI Agent logic & security

frontend/src/
├── terminal.ts             xterm.js wrapper
├── tab-manager.ts          tabbed session manager
├── sftp-panel.ts           SFTP manager
├── server-list.ts          server management
├── auth-form.ts            anon connect/local creds
├── i18n/                   Chinese/English
└── agent/                  AI Agent UI panel

docs/theme-editor/           Online theme editor
Architecture overview
Architecture
│
├── Browser client
│   ├── Web SSH terminal
│   ├── SFTP manager
│   ├── Multi-tab sessions
│   ├── AI Agent panel
│   └── Themes & i18n
│   │
│   └── Connect down via HTTPS/WebSocket
│
├── Cloudflare Worker
│   ├── API routing
│   ├── GitHub OAuth
│   ├── Turnstile challenge
│   ├── Rate limit
│   ├── Origin check
│   └── One-time token route
│   │
│   ├── Route to ──► SSHSessionDO
│   └── Route to ──► UserDBDO
│
├── SSHSessionDO (session mgmt)
│   ├── SSH session lifecycle
│   ├── TCP socket
│   ├── SSH-2.0 protocol
│   ├── SFTP subsystem
│   ├── Agent exec channel
│   ├── SSRF/DNS checks
│   └── Terminal context
│   │
│   ├── SSH/TCP connect ─► target server
│   └── HTTPS connect ─► user LLM service
│
└── UserDBDO (persistent data)
    ├── User/session
    ├── Server configs
    ├── AES-GCM secrets
    ├── Known hosts
    ├── Themes
    └── AI config
Who is it for?
- Individual developers: Manage personal VPS, cloud hosts, dev envs
- Ops staff: Emergency operations when SSH client isn’t handy
- Mobile/on-the-go users: Check server status via tablet/phone
- Small teams: Deploy as a lightweight server management portal
- Open source learners: Study Cloudflare Workers, Durable Objects, SSH, SFTP protocols
- AI Ops explorers: Try LLM + SSH tool workflows with agent
For team/production use, configure GitHub OAuth, Turnstile, strict host key checks, and custom access control—and harden further as needed.
Finally
CloudSSH doesn’t aim to replace full-featured desktop SSH clients.
It’s a handy alternative portal you can use anytime:
- When you can’t install a client, just open a browser
- Need to move a few files? Open SFTP
- Managing several servers? Use multi-tab mode
- Not sure where to start troubleshooting? Let AI Agent help
If you find this project useful, star it on GitHub:
Issues and PRs welcome!
Relevant links
- GitHub repo: GitHub - newbietan/CloudSSH: Serverless Web SSH client built on Cloudflare Workers with a pure TypeScript SSH stack, multi-session terminals, SFTP file management, and an AI operations assistant. 基于 Cloudflare Workers 的无服务器 Web SSH 客户端,支持多会话终端、SFTP 文件管理与 AI 运维助手。 · GitHub
- Online version: https://ssh.newbietan.cn/
- Online test: https://sshtest.newbietan.cn/
- Online theme editor: CloudSSH Theme Editor
- Demo video: https://www.bilibili.com/video/BV1UgMt6UEdF
Please refer to the repo docs
The project is being updated continuously; for deployment reqs, security, and features, always consult the latest README and CHANGELOG in the GitHub repo.
Open your browser, connect to your server. It’s really that simple.


