【Important Security Notice】Gleam Free Second-Level Domain Data Breach Incident
Published: 2026-09-18
What Happened
We have confirmed that the Gleam service experienced a data breach.
Our investigation found that the breach was not caused by a server intrusion. Instead, the ZCode editor used in the development environment automatically packaged, encrypted, and uploaded the working directory to its server-side object storage (Alibaba Cloud OSS) without clearly notifying users or obtaining authorization. The uploaded directory contained project source code, configuration files, backup repositories, and user data.
Data Potentially Involved
The following information may have been affected:
- Users’ registered email addresses
- User avatars
- Hashed passwords for some users (not in plaintext, but potentially vulnerable to offline cracking)
- Domain DNS records for all users
- 2FA data for some users (stored in encrypted form, but the server-side decryption method was also included in the breach, meaning the 2FA seeds may have been exposed)
- The entire system source code
- Multiple backup repositories
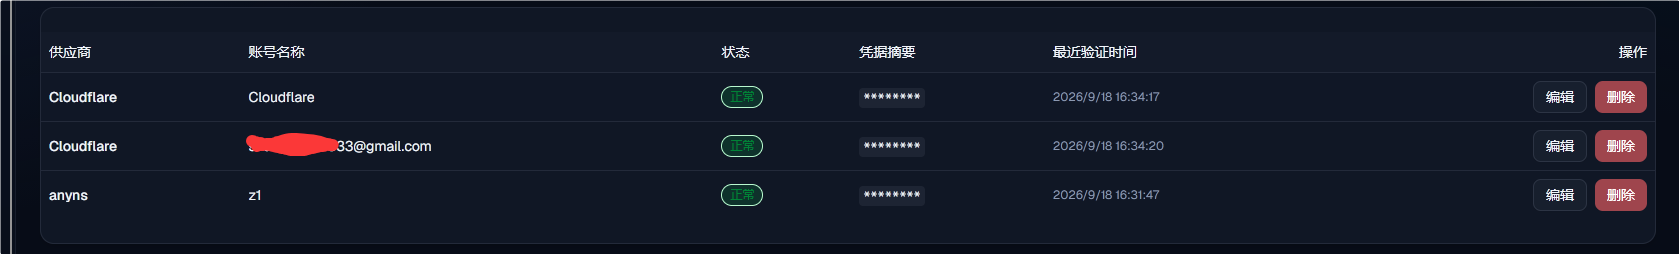
- The server’s old Cloudflare API Key (revoked and replaced)
- AnyNS Key (revoked and replaced)
Measures Taken
 The Cloudflare API Key has been replaced, and the old key is no longer valid
- The AnyNS Key has been replaced, and the old key is no longer valid
- The source of the breach has been blocked, and residual data waiting to be uploaded locally has been removed
 We are assessing whether to force all users to reset their passwords and 2FA; a separate announcement will be issued once a decision is made
What You Should Do
- Change your Gleam account password as soon as possible. If you use the same or a similar password on other sites, change it there as well—this is the most important step.
- If you have enabled 2FA, set it up again. Since the decryption method may have been exposed, your old 2FA setup can no longer be trusted.
- Watch out for phishing emails. Your registered email address and DNS records may have been exposed. Do not trust any email claiming to be official that asks for your password or verification code.
- If you used the same email address to register for other services, watch for suspicious login alerts.
Apology
The essence of this incident is that we entrusted a working directory containing user data to a tool that secretly uploaded data, and we failed to detect it promptly. Regardless of the breach path, protecting user data is our responsibility—and this time, we failed to do so. We are deeply sorry.
Investigation results and follow-up progress will continue to be updated in this thread.
Images below
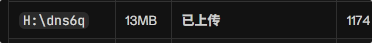

All keys have been replaced. We will improve encryption and investigate more software that may have leaked data in the near future. Disgusting ZCode.