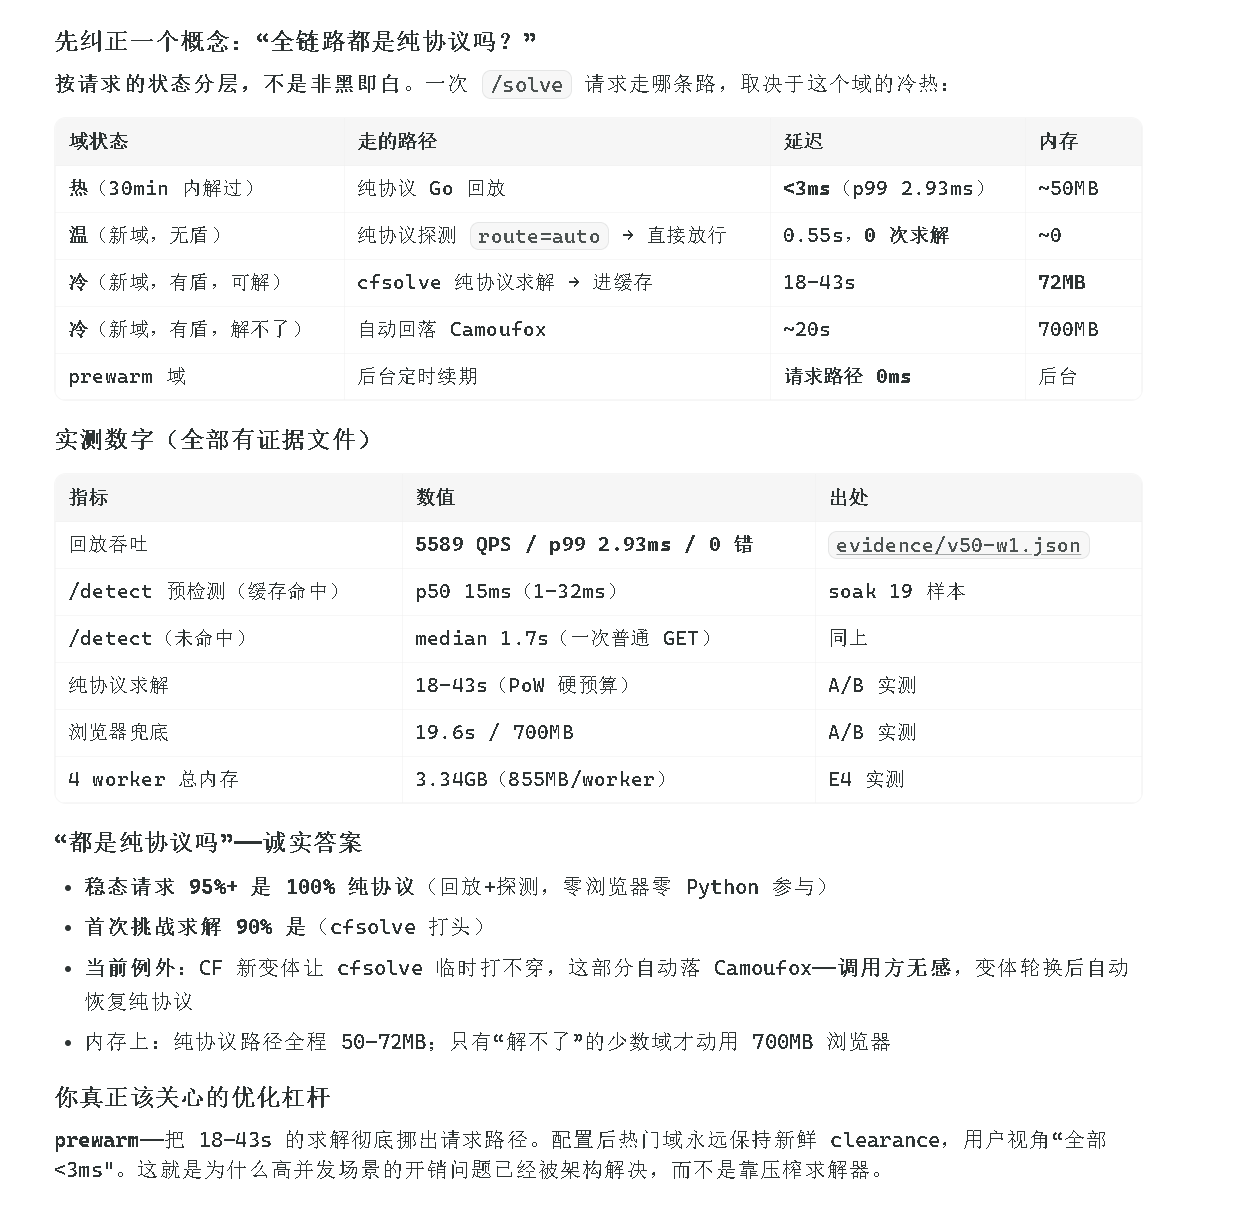
I did my best, guys—purely protocol-based, just solving the CF human verification.

I don’t believe those claims about passing in one, two, or three seconds. Just give them an unfamiliar website and see whether they can pass it instantly on the first try.

It turns out they all need to pass it once initially, then keep a recording, and only after that can they pass it instantly.
17 Likes

Couldn’t find any assets from previous contributors, or is CF still being updated? :thinking:

Thanks for sharing

:xhj001:What is this for?

Thanks for sharing

Pure protocol, no headless browser?

CF keeps updating its variants, which means constantly compiling, reverse-engineering, and updating. There’s never a stable method.

It’s just a pure protocol. Go ask the AI in the Git repository.

Learn a bit.

Want to take on a CF challenge? It’s kind of interesting.

Thanks for the red envelope.

That’s fucking awesome. :04-zan:

Thanks for sharing!

Looks interesting. Can it pass Linux.do’s CAPTCHA?

Go take a look

Thanks for sharing

Nice. The previous solutions all ran through a browser.

Saluting the big shot (just here to snag a red envelope).

When will there be a purely computational solution for hCaptcha? People have suffered from it for far too long.

1 Like

As always :+1: